IT solutions for banks, insurers and financial service providers
Digital resilience and regulatory certainty for companies with critical infrastructure.
Digitalisation, new regulatory requirements, cyber risks, ESG criteria and the shortage of skilled staff put banks, insurers and financial service providers under pressure. Security, availability and resilience must be right, and the number of legal obligations keeps growing. We provide stable, scalable and compliant IT services that strengthen the efficiency and compliance of your critical infrastructure.
- BAIT, VAIT, ZAIT, DORA and GDPR
- ESG standards and critical infrastructure
- At the side of regulated financial organisations for over 25 years
Your challenges in IT operations
Hybrid IT environments, legacy systems and cloud solutions must work together smoothly. Frameworks such as BAIT, VAIT, ZAIT, DORA, ISO 27001 and critical infrastructure rules demand traceable processes, continuous monitoring and documented resilience. This is often the starting point in regulated IT environments:
Technology mix
IT environments that have grown over time, with legacy and cloud systems.
Compliance pressure
Meeting DORA, BAIT, VAIT, ZAIT, ISO 27001 and critical infrastructure rules at once.
Stability demands
High availability, complete monitoring and short response times.
Efficiency pressure
Relieving day-to-day operations, automating and consolidating tools.
This is exactly where we come in: with managed services tailored to your needs, intelligent automation and secure operating models. This way your IT keeps pace with the demands of the industry or stays ahead of them.
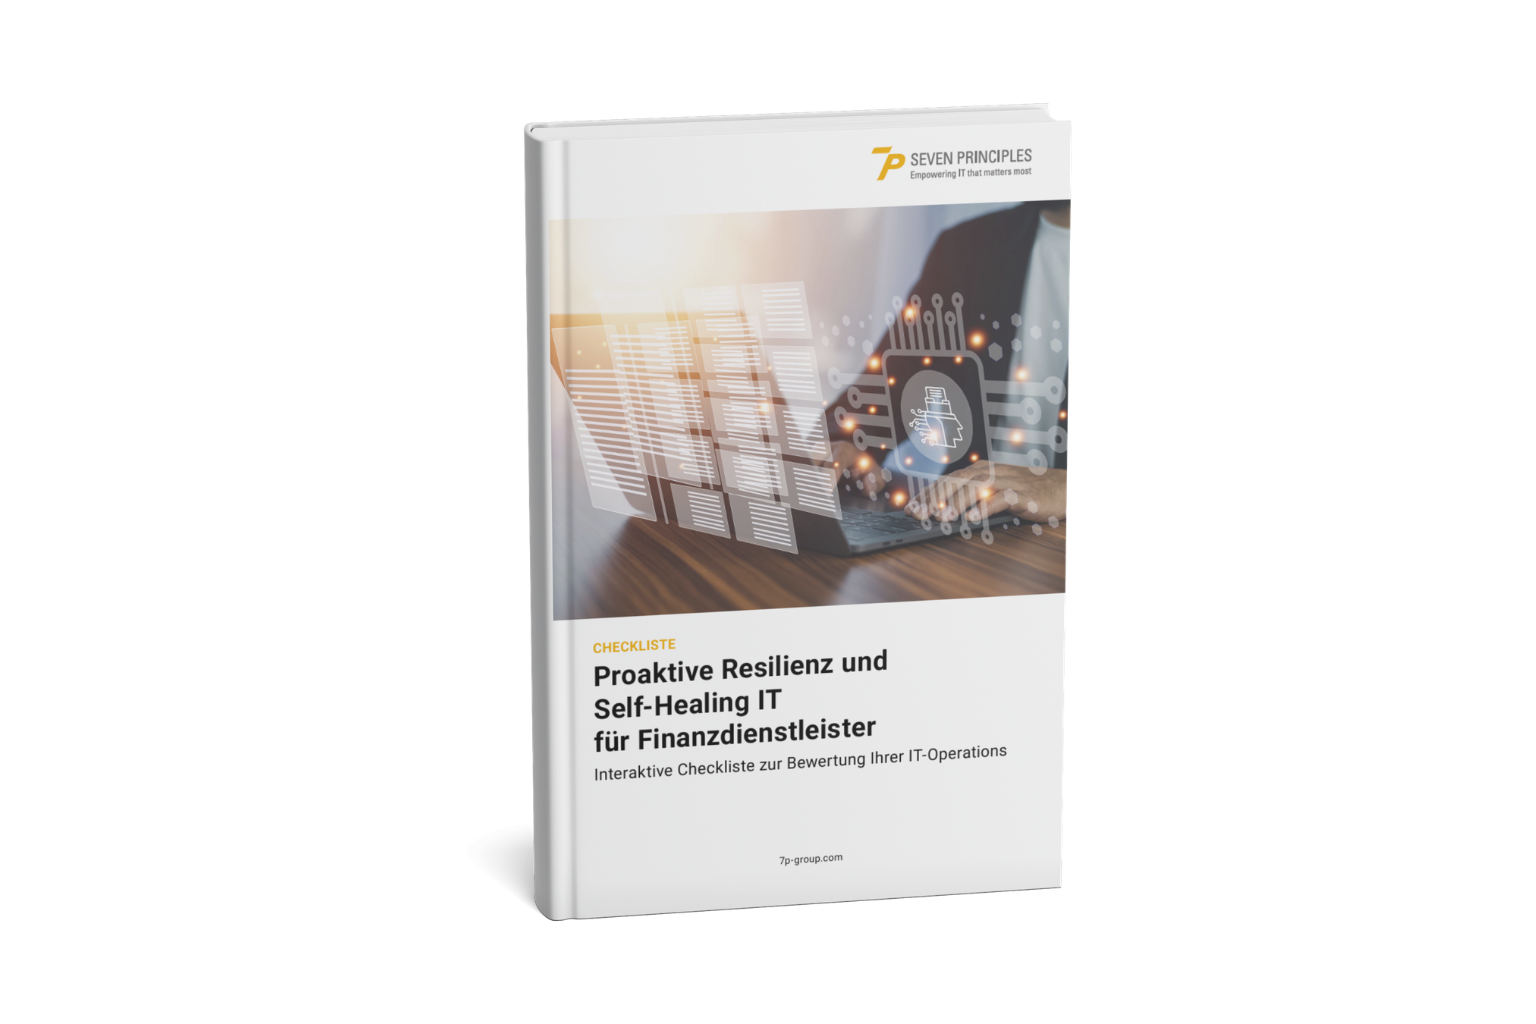
How resilient are your IT operations really?
Our checklist “Proactive resilience and self-healing IT for financial service providers” shows you. With 20 concrete criteria, you assess the maturity of your IT operations and identify structural weaknesses early.
Noch zu ergänzen: Link zum Download der Checkliste IT-Resilienz für Finanzdienstleister
Your role in focus: IT responsibility under competing demands
IT managers stand between regulatory control, technical complexity and growing pressure to innovate. BAIT, DORA and other requirements demand traceable processes and maximum stability. At the same time, systems should stay flexible and become more efficient. We help IT leaders manage complexity without losing agility.
Operational stability and speed of innovation
Modular operating models and our experience with legacy environments secure ongoing operations and make room for new things, for example through step-by-step migrations, zero-downtime approaches and cloud-ready architectures.
Compliance and flexibility
Our services combine ITSM standards with regulatory know-how. Compliance by design with audit-proof documentation, ISAE 3402 reporting and aligned IT governance, without limiting your ability to change.
Cost efficiency and availability
Managed services tailored to your needs, AIOps-supported monitoring and scalable operating models reduce your operating effort measurably. The result is availability with clear SLAs and without unnecessary cost blocks.
Industry expertise for regulated organisations
Bank, insurer or financial service provider: in highly regulated markets, the quality of IT determines the ability to act, audit security and readiness for the future. Established systems must run stably and be modernised at the same time. Requirements such as BAIT, VAIT, ZAIT or ESG guidelines must be implemented on an ongoing basis. And digital services should be efficient, secure and compatible.
How long have you worked for the financial sector?
Our teams have supported regulated financial organisations through transformation for over 25 years. For us, modernisation is not a single project but a process that evolves on a sound, methodical and integrated basis.
Which standards do you implement?
We implement regulatory requirements in line with ISAE 3402, ISO 27001 and ISO 9001. DORA, critical infrastructure rules and ESG are not buzzwords for us but part of everyday delivery.
How do you make audit readiness measurable?
With dashboards that make audit readiness visible, and automated reporting processes. We also support the design of resilient system architectures and the introduction of service controlling and GRC mechanisms.
What does future-ready IT operations involve?
Future-ready operating models, audit-proof reporting structures and transparent, scalable ITSM architectures. This is how we bring regulatory duty and operational reality together and make room for new things.
Our sites are certified to ISO 9001 and ISO/IEC 27001. We have our internal control systems assessed regularly by external auditors to ISAE 3402. More on certificates and compliance
Let us talk
DORA requirements, ITSM optimisation or legacy modernisation: together with you, we develop the right solution with clearly measurable results.
Your contact: Oliver Feil, Corporate Development Executive.
Our services for financial organisations: 360° consulting,software development, managed services andAI for Enterprise.
Talk to us about your IT operations
Our experts answer your questions on IT operations, compliance and modernisation.